 Write a Review
Get Demo
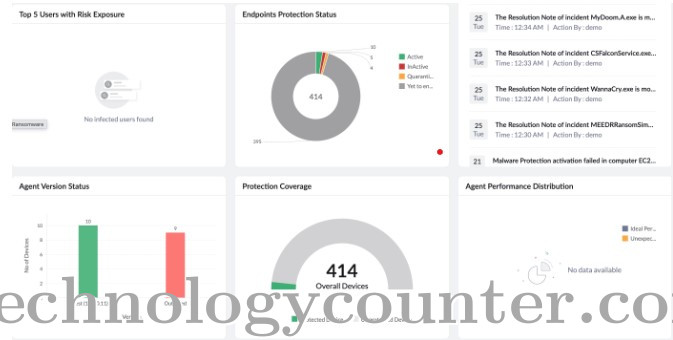
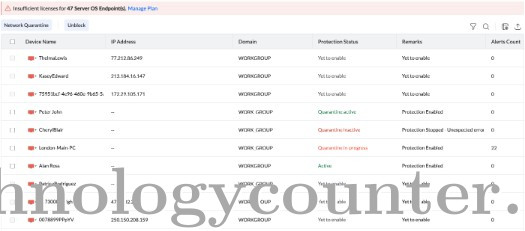
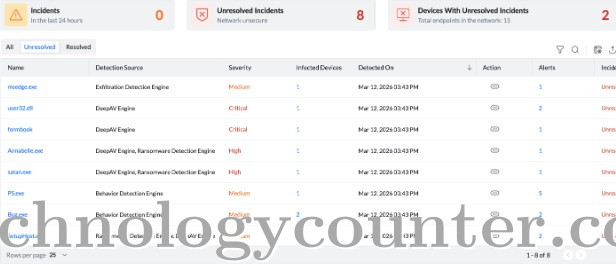
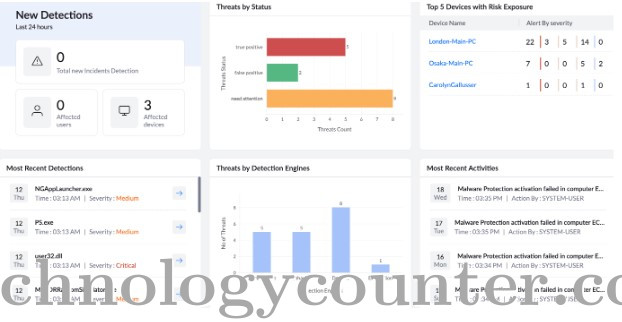
ManageEngine Malware Protection Plus (MPP) is an enterprise NGAV solution that goes beyond traditional signature-based detection, combining AI-driven intelligence, behavioral analysis, and exploit prevention into a unified endpoint security framework.
Its multilayered detection includes:
Exploit Protection to block vulnerability-based intrusions
DeepAV Engine using machine learning and deep neural networks for zero-day threat detection
Behavioral Detection monitoring processes, registry changes, and network anomalies
Ransomware Detection with real-time encryption monitoring and decoy files
Data Exfiltration Detection identifying unusual outbound transfers
When a threat is detected, MPP conducts root cause analysis aligned with the MITRE ATT&CK framework, isolates compromised endpoints, terminates malicious processes, and automates remediation — restoring files, registry entries, and configurations.
Built-in rollback capabilities reverse ransomware encryption and unauthorized changes, ensuring business continuity with minimal disruption and data loss.
Be the first to leave a review for ManageEngine Malware Protection Plus
Write a ReviewYes! Malware Protection Plus offers a 30-day free trial with full access to all features with no credit card required. You can evaluate the platform across your entire network before committing to a plan.
It combines AI/ML algorithms, behavioral detection, and real-time threat analysis to identify known, unknown, zero-day, and fileless threats.
Traditional antivirus primarily uses signatures, while Malware Protection Plus combines signatures, AI-driven behavioral analysis, and advanced detection for evolving threats.
Yes. On-device detection logic continues protecting endpoints when they are offline or connected to untrusted networks.
Yes. It uses behavioral and memory-based detection to identify malicious activity that executes without leaving traditional files on the endpoint.
It detects ransomware behavior, blocks malicious processes, prevents encryption, and can roll back affected files to their pre-attack state.